AI · Edge · Community

Know if a site is trustworthy
before you interact

A Chrome extension that analyzes every domain you visit and shows a real-time trust score — powered by AI on Cloudflare's global edge network.

Built by Keerti Panchakshari Charantimath  ·  LinkedIn
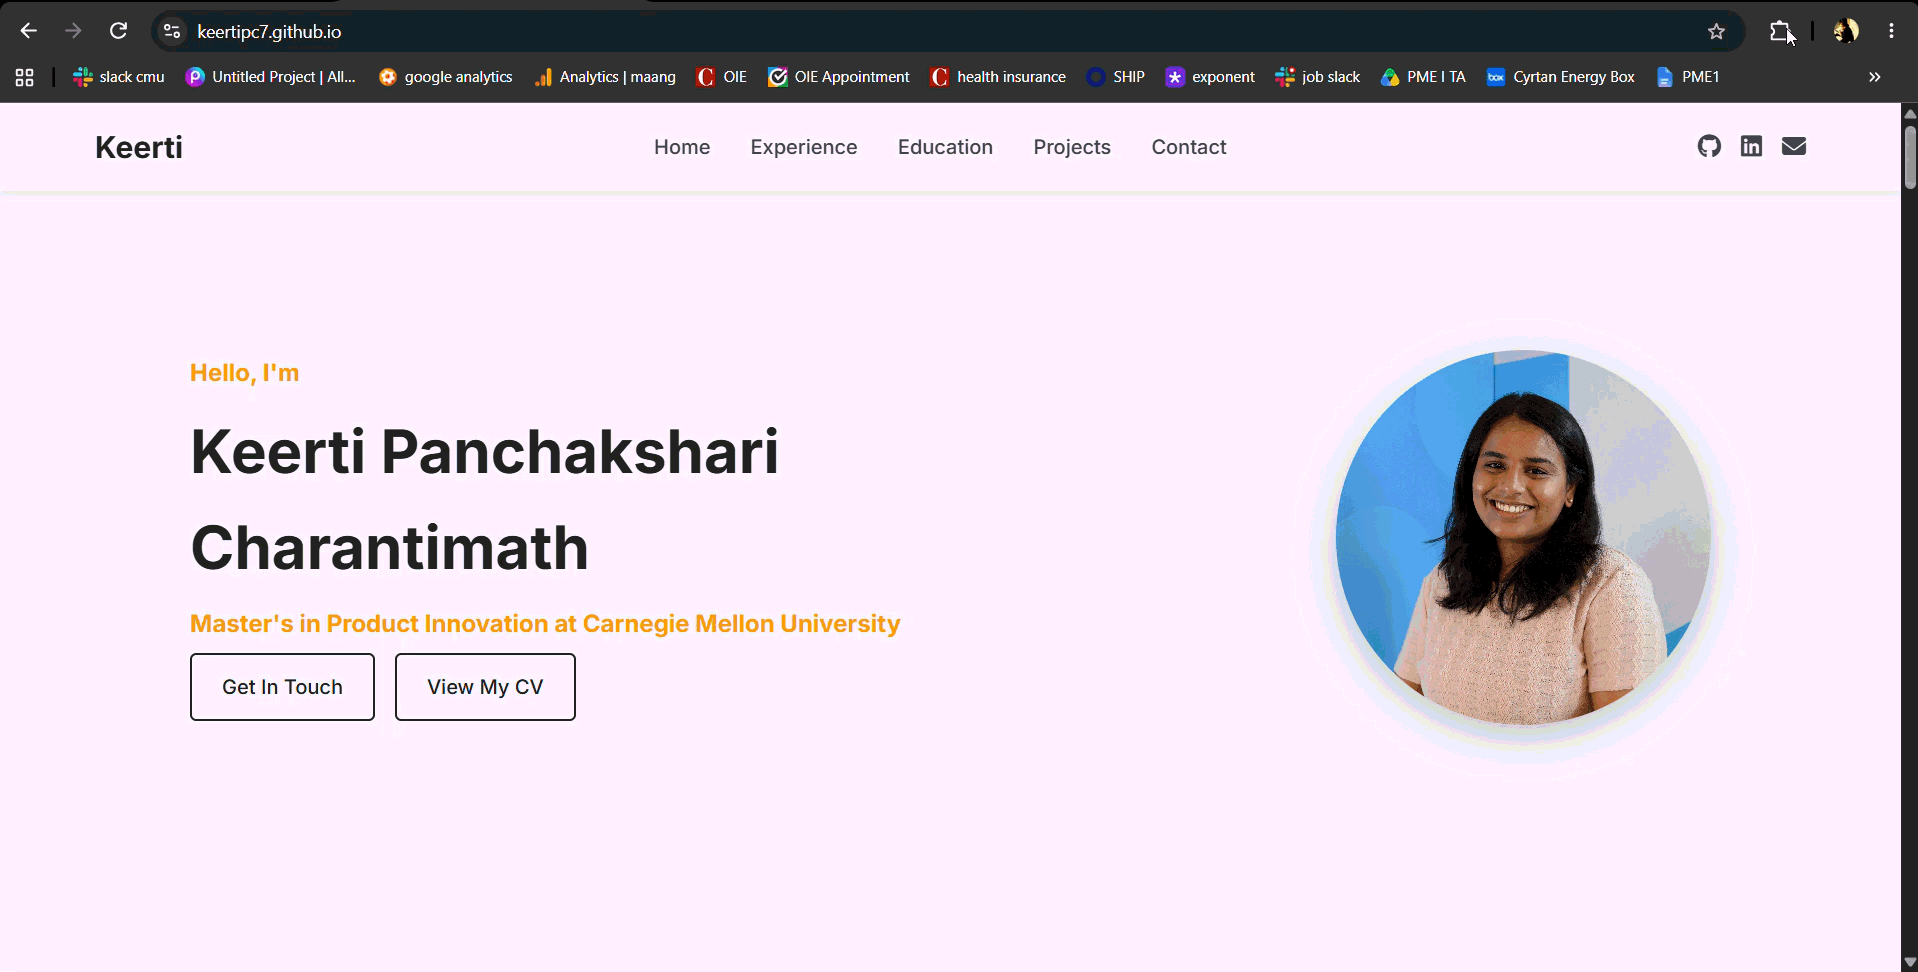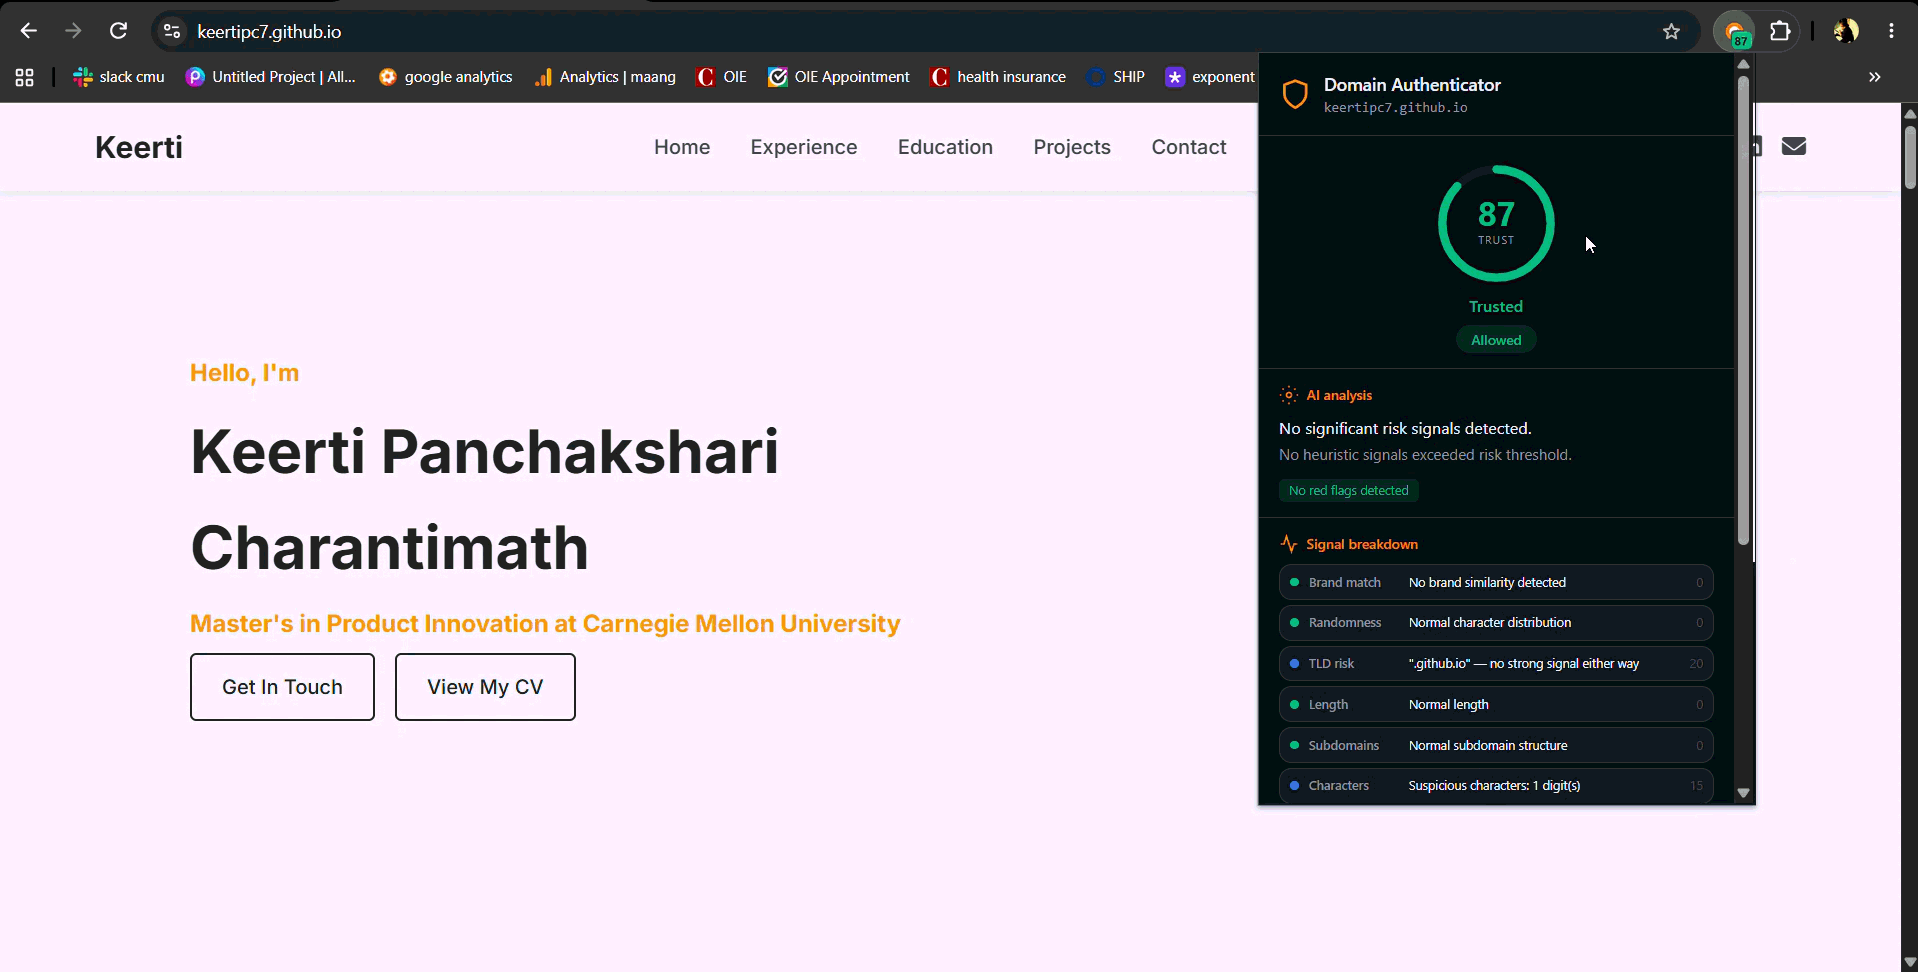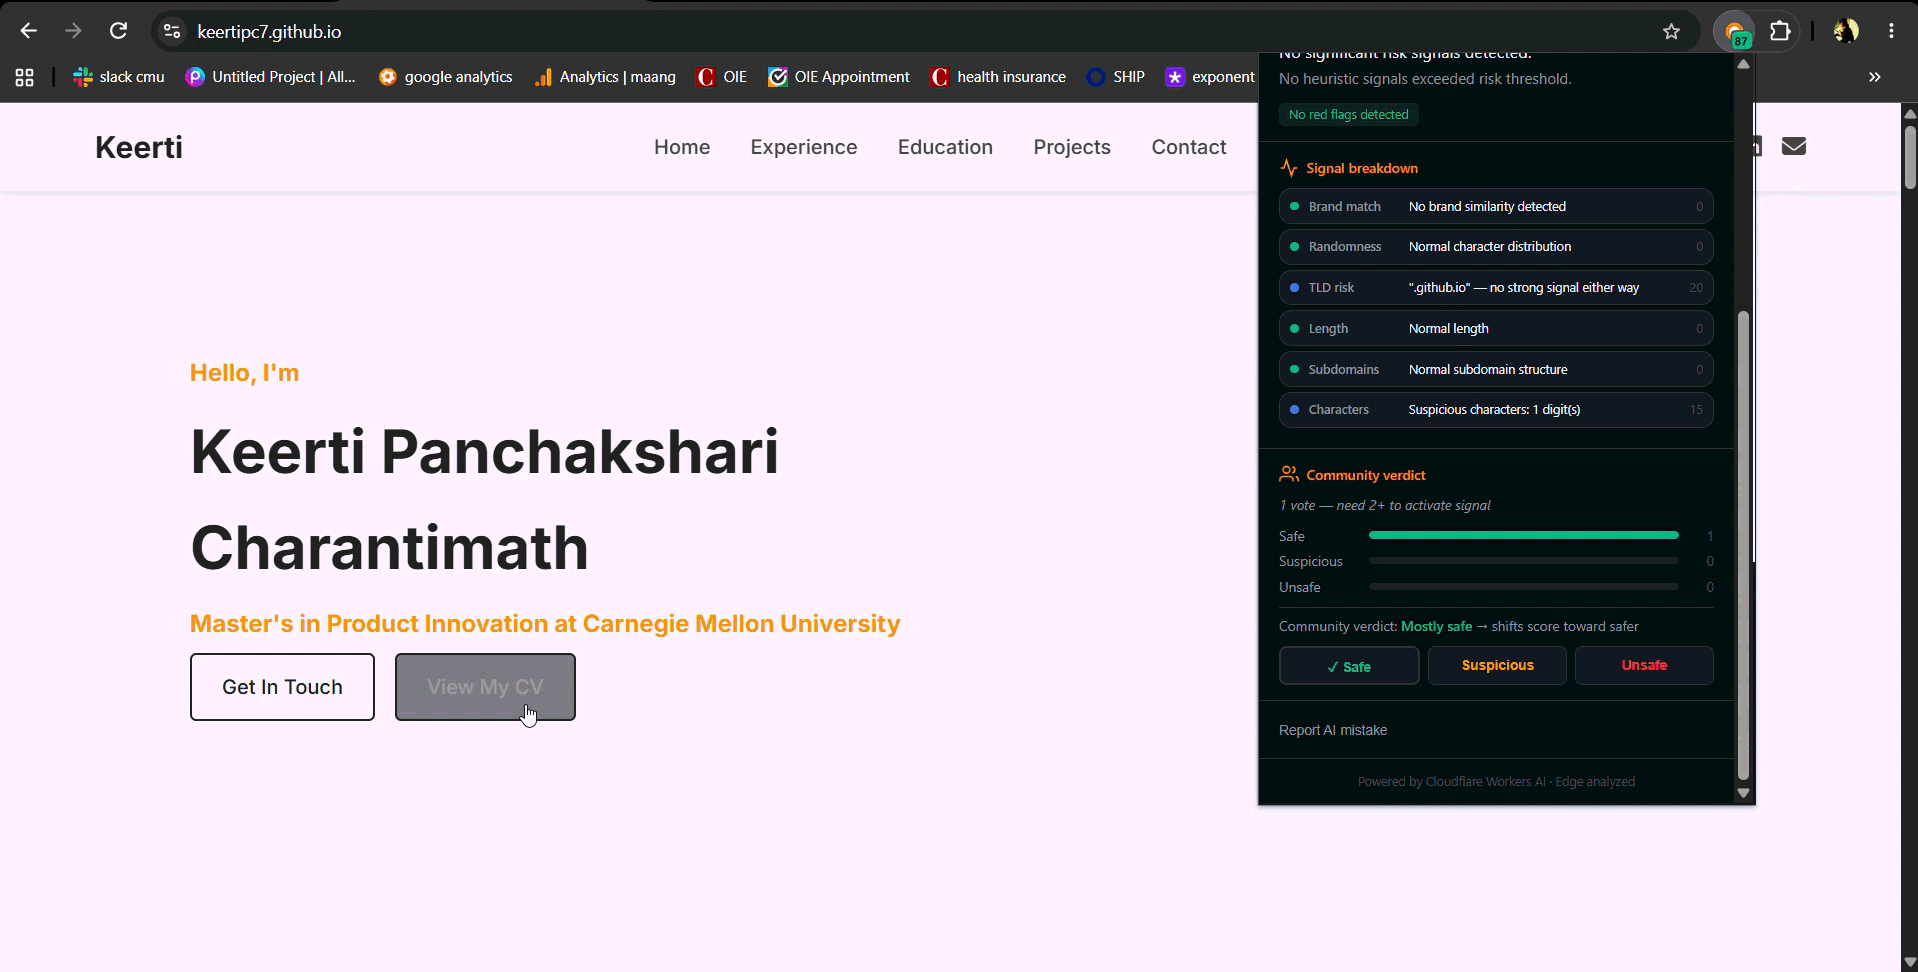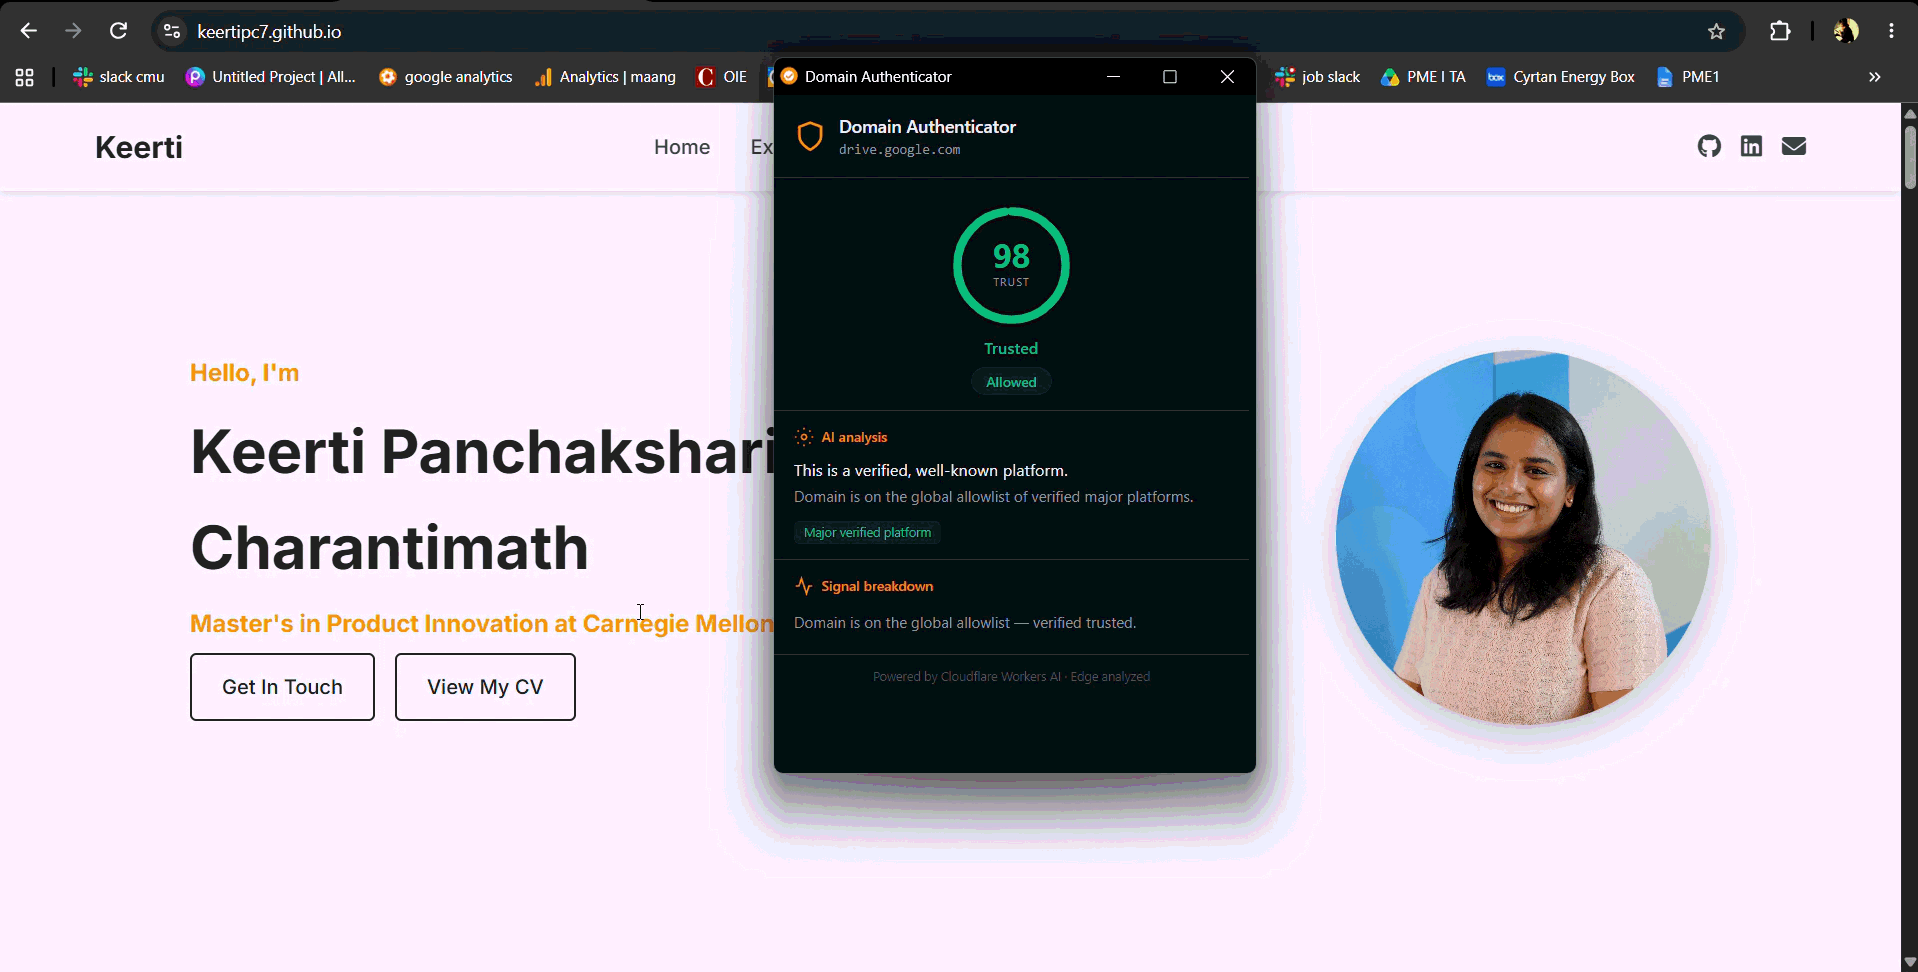
Domain Authenticator demo
LIVE API Score calculated at the edge in real time

How to use

Two ways to check a domain

Trust scores surface right where you need them — no extra steps required.

01

Assess the site you're on

Open the browser extension on your current site to check its safety.

Extension badge showing trust score
02

Assess before you click

Right-click any link to check its safety before navigating to the page.

Right-click context menu with Analyze link safety

How the score is calculated

From click to trust score

Every domain runs the same three-stage pipeline, cached at the edge for speed.

01

User navigates

Domain captured from the active tab and sent to POST /analyze.

02

Cloudflare Worker analyzes

① Heuristics — brand, TLD, entropy  →  ② Workers AI (Llama 3.1 8B)  →  ③ Community votes, weighted.

03

Workers KV cache check

Cached? Return instantly. New? Run the pipeline and store the result for 6 hours.

Result

Trust score, 0 – 100

● 75–100 Trusted  ·  ● 42–57 Caution  ·  ● 0–21 Dangerous


The problem

Phishing works because defenses lag

The average phishing site is live for 21 hours before any blocklist catches it.

01

Blocklists are reactive

Safe Browsing only catches reported domains — hours after they're live.

02

Typosquatting costs $1

Registering g00gle.xyz takes seconds. Most users won't notice.

03

Network tools are blind to the browser

A page that loads clean HTML and renders a phishing form via JavaScript is invisible to proxies.

The white space

Nobody scores domains at navigation time

No tool combines AI + community signals at the browser layer, in real time, at the moment you click.

Network layer — firewalls, DNS, proxies
Sees HTTP payloads. Blind to client-side JavaScript rendering.
Existing
Device layer — endpoint agents
Sees OS state. Can't see inside a browser tab.
Existing
Browser layer — Domain Authenticator
Analyzes domains at navigation time. Surfaces risk before you interact.
This tool

Who it's for

Anyone who clicks links

Especially useful for high-value targets and security teams.

👩‍💼
Enterprise employee

Handles sensitive data daily

Gets phishing emails mimicking internal tools. Needs protection that requires no behavior change.

🔐
IT / Security admin

Owns their org's security posture

Wants a browser-layer signal to act on — warn or isolate — within their existing policy engine.

🧑‍💻
Developer / power user

Clicks dozens of unfamiliar links daily

Wants a fast check on links from Slack, GitHub, or email before navigating.


Features

What it does

Each feature closes a specific gap.

Trust score badge on every tab

Color-coded score updates automatically on every navigation. Green = trusted, red = dangerous.

Warning banner on suspicious sites

Amber banner injected at the top of the page for caution-level domains. Dismissible, auto-disappears after 10s.

Full analysis in the popup

Click the shield icon for the complete breakdown — trust gauge, per-signal scores, plain-English AI explanation.

Community voting

Vote Safe / Suspicious / Unsafe from the popup. Weighted votes from real users feed back into scoring.

Report AI mistakes

Flag wrong verdicts directly from the popup. Creates a feedback loop that improves accuracy over time.

Scoring model
Brand similarity
30%Typosquatting, digit substitution (g00gle)
AI verdict
22%Semantic patterns heuristics miss
TLD risk
18%.xyz, .top, .buzz and 30+ high-abuse TLDs
Entropy
10%DGA-generated random-looking domains
Subdomain abuse
10%paypal.com.evil.xyz patterns
Characters + length
10%Hyphen/digit abuse, unusual length
Combo override: digit substitution of a known brand on a high-risk TLD forces a dangerous verdict immediately.

Community voting

AI starts it. Humans refine it.

Community votes correct AI mistakes — especially on brand-new domains with no threat-feed history.

STEP 1

Visit a domain

AI + heuristics produce initial verdict

STEP 2

Cast a vote

Safe, Suspicious, or Unsafe

STEP 3

Vote is weighted

Active reviewers carry up to 2×

STEP 4

Consensus shifts score

60%+ majority escalates or de-escalates

⚖️
Weighted votes — New users: 1×. 10+ reviews: 1.5×. 50+: 2× (capped).
🔢
Minimum threshold — Needs 2+ votes before community signal activates.
🔼
Unsafe majority — 60%+ unsafe votes shifts scoring toward higher risk.
🔽
Safe majority — 60%+ safe votes with 50%+ confidence shifts scoring toward lower risk.
🔄
Cache busts on vote — Next visitor gets fresh analysis reflecting new community data.